Standards note
The ASVS penetration test: verifying an application by level
An ASVS penetration test checks a web application against the OWASP Application Security Verification Standard. So results map to defined requirements, and progress can be measured release by release.
- Written scope and rules of engagement
- PTES, OWASP and NIST SP 800-115
- Nothing retained after close
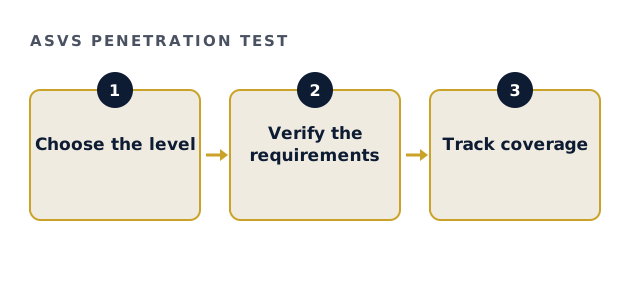
What makes an ASVS penetration test different
A typical test lists what the tester found. In contrast, ASVS verification asks whether each requirement holds. Therefore you learn both what failed and what was confirmed.
That suits teams that need a repeatable baseline. Also, it gives developers a checklist they can build against.
Choosing the level for an ASVS penetration test
ASVS defines three levels. However, the level should follow risk, not ambition.
| Level | Typical use |
|---|---|
| Level 1 | Baseline for most applications |
| Level 2 | Applications handling sensitive data |
| Level 3 | High-value or critical applications |
ASVS penetration test readiness check
Tick what you can provide.
Your result appears here as you tick, so you can see what is still open.
What an ASVS penetration test covers
Requirements span the application. For example, authentication, session management, access control and input handling.
- Authentication and session management
- Access control
- Validation and output handling
- Cryptography and data protection
- Configuration and error handling
Reading the results
Results show pass, fail or not applicable for each requirement. As a result, coverage becomes visible, and gaps are easy to plan around.
In addition, retests can target failed requirements only. The standard is published as the OWASP Application Security Verification Standard.
How Certus works
Each engagement names its verification level in the written scope. Full engagements usually settle between $35,000 and $120,000, and the floor is $25,000. The bounded Security Posture Assessment starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days.
Also build the level into development. Because developers can use ASVS requirements as acceptance criteria, many issues never reach the test. So verification becomes confirmation rather than discovery. In addition, record exceptions with a reason, because some requirements may not apply.
ASVS penetration test questions
Is an ASVS penetration test better than a standard test?
It is more structured, which suits teams wanting measurable coverage.
Which level should an ASVS penetration test use?
The level that matches the application's risk.
Does an ASVS penetration test include source code review?
Some requirements are easier to verify with code access, so grey-box work helps.
Can results support audits?
Yes. Requirement-level results are easy for reviewers to follow.
Related guides
Scope an ASVS penetration test
Tell us the application and the level you need. We return a written scope with a fixed fee. Nothing is tested before the owner signs.
Request a written scope