Engagement type
OWASP penetration testing: what the method covers, and what it does not
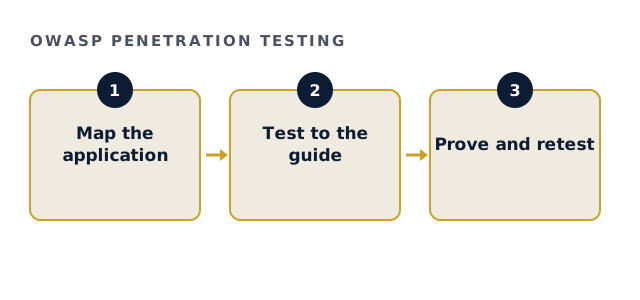
OWASP penetration testing means testing web applications and APIs against the methods the OWASP community publishes. So the label is only meaningful when the report shows which tests were run and what they proved.
- Written scope and rules of engagement
- PTES, OWASP and NIST SP 800-115
- Nothing retained after close
Three OWASP documents, three different jobs
People often say OWASP when they mean the Top 10. However, the Top 10 is an awareness list, not a test plan. Instead, the documents that actually govern OWASP penetration testing are these three.
| Document | Purpose | Use in a test |
|---|---|---|
| Web Security Testing Guide | A structured testing method. | Defines what is tested and how. |
| ASVS | Verification requirements by level. | Sets the depth to aim for. |
| Top 10 | The most common risk categories. | A summary lens, not a checklist. |
What OWASP penetration testing examines
The OWASP Web Security Testing Guide groups the work into areas an attacker would probe first. For example:
- Authentication and session handling
- Authorisation, including access to other users' data
- Input handling and business logic
- Configuration, error handling and cryptography
- API endpoints and the trust they place in the client
Ready to scope OWASP penetration testing?
Tick what you can provide. Each item makes the written scope sharper.
Your result appears here as you tick, so you can see what is still open.
Where OWASP penetration testing needs judgement
Business logic is the hard part, because no tool understands your rules. A scanner cannot know that an approval step should never trust a value sent by the browser. So every finding is validated by hand, and related findings are chained into the route an intruder would take.
Also, the OWASP Application Security Verification Standard helps agree depth in advance. Therefore you know before testing starts whether the goal is a baseline check or a deeper verification.
What the OWASP penetration testing report contains
Also, each finding carries reproducible steps, business impact and a fix. In addition, the report states which parts of the guide were in scope, so gaps are visible rather than hidden. A complimentary retest then confirms the fixes.
Fees and fit
Full engagements usually settle between $35,000 and $120,000, and the floor is $25,000. The bounded Security Posture Assessment starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days. A single application often fits a full engagement near the floor, while a large estate sits higher.
OWASP penetration testing questions
Is OWASP penetration testing the same as checking the Top 10?
No. The Top 10 summarises risks, while the testing guide defines the actual tests.
Does OWASP penetration testing cover APIs?
Yes. APIs are tested alongside the application, including authorisation between users and roles.
Do you test in production?
Only where the owner agrees it in writing. Otherwise a staging copy is preferred.
How long is the report kept?
It is delivered over encrypted channels, and evidence is destroyed when the engagement closes.
Related guides
Request a written OWASP scope
List the applications and roles in scope. We reply with a written scope, the OWASP areas covered and one fixed fee. Testing starts only after the owner signs the authorisation.
Request a written scope