Standards note
Vulnerability assessment and penetration testing: two halves, two different proofs
Vulnerability assessment and penetration testing, often shortened to VAPT, combines breadth with depth. So the first half finds what is exposed, while the second proves what an intruder could actually reach.
- Written scope and rules of engagement
- PTES, OWASP and NIST SP 800-115
- Nothing retained after close
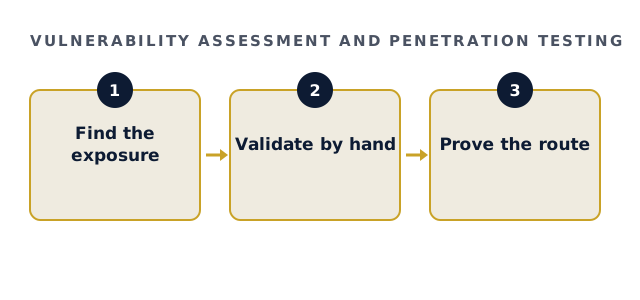
What each half of the work proves
However, the two halves answer different questions. Therefore a proposal should say how much of each it includes.
| Vulnerability assessment | Penetration testing | |
|---|---|---|
| Question | What weaknesses exist? | What could an intruder reach? |
| Method | Broad, tool-assisted, then reviewed. | Manual-led, chaining findings. |
| Output | A prioritised list. | A proven route with evidence. |
How vulnerability assessment and penetration testing is scoped
Scope starts with an inventory, because the assessment can only cover what is listed. Then the testing half focuses on the systems where a breach would cost most. As a result, breadth and depth are both planned rather than left to chance.
Plan your vulnerability assessment and penetration testing
Tick what you already have. Open items extend the scope.
Your result appears here as you tick, so you can see what is still open.
Where the standards place each half
NIST SP 800-115 describes review techniques, target identification and vulnerability validation as distinct stages. Similarly, the Penetration Testing Execution Standard separates vulnerability analysis from exploitation. So a combined engagement follows a recognised sequence, not an improvised one.
Reading a vulnerability assessment and penetration testing report
So look for two things. First, every assessment finding should be validated by hand, because unvalidated tool output creates noise your engineers must disprove. Second, the testing section should show routes, not just items, with reproducible steps and a fix for each.
Also check that severity uses a recognised scale such as CVSS, maintained by FIRST.
Fees and the bounded option
Full engagements usually settle between $35,000 and $120,000, and the floor is $25,000. The bounded Security Posture Assessment starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days. The bounded assessment covers up to five external hosts and one public web application, with a report in five business days.
Vulnerability assessment and penetration testing questions
Is vulnerability assessment and penetration testing one service or two?
Usually one engagement with two stages, so the scope should state how much effort goes to each.
Can a scan replace the testing half?
No. A scan lists issues, while testing proves what they allow together.
How long does vulnerability assessment and penetration testing take?
It depends on scope. The bounded assessment reports within five business days.
Is the bounded assessment enough for SOC 2 or PCI?
No. Auditor-grade evidence needs the full engagement.
Related guides
Request a written VAPT scope
Send your inventory or a short description. We reply with a written scope that splits breadth and depth, and one fixed fee agreed before testing.
Request a written scope