Engagement type
Purple team penetration testing: attack and defence in the same room
Purple team penetration testing runs offensive work in the open, alongside your defenders. So instead of asking only what an intruder could reach, it also asks what your team saw, and what it missed.
- Written scope and rules of engagement
- PTES, OWASP and NIST SP 800-115
- Nothing retained after close
How purple team penetration testing differs
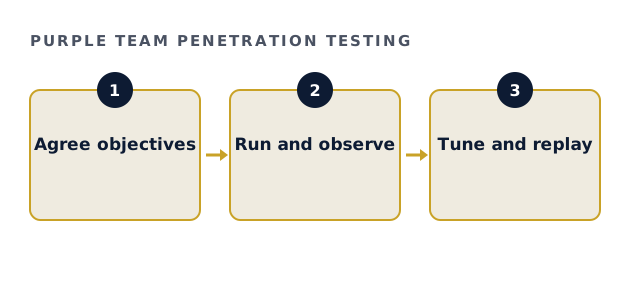
In a red team simulation, defenders usually do not know the timing. By contrast, a purple team works collaboratively, step by step. As a result, every action becomes a chance to check a detection.
| Red team | Purple team | |
|---|---|---|
| Defenders informed? | Usually not. | Yes, throughout. |
| Main question | Can the objective be reached? | Is each step detected? |
| Output | Attack path and impact. | Detection gaps and fixes. |
Why ATT&CK mapping matters in purple team penetration testing
MITRE ATT&CK gives attackers and defenders one vocabulary. Therefore each step of the exercise is labelled, and your team records whether it was logged, alerted or missed. Then the results form a coverage map rather than a story.
Is purple team penetration testing right for you now?
Tick what is already true. Fewer ticks suggest starting with a standard test.
Your result appears here as you tick, so you can see what is still open.
What purple team penetration testing needs from you
However, the exercise depends on your defenders being available. So it pays to agree the following in the rules of engagement:
- Which detection and response staff take part
- Which objectives and behaviours are in scope
- Testing windows and a stop procedure
- Where logs and alerts are reviewed together
What you receive
Then you receive the attack steps, the detection result for each, prioritised fixes and a written debrief. In addition, steps that were missed can be replayed after tuning. So the improvement is measured, not assumed.
Fees for purple team penetration testing
Red team and purple team work begins above the $25,000 floor, because objectives and rules take more preparation. Full engagements usually settle between $35,000 and $120,000, fixed after a written scoping brief.
Purple team penetration testing questions
Is purple team penetration testing better than a red team?
It answers a different question. A red team tests the objective, while a purple team improves detection step by step.
Do we need a security operations team?
Some detection capability is needed. Otherwise a standard penetration test is the better first step.
Can purple team penetration testing use our own scenarios?
Yes. Objectives and behaviours are agreed in writing during scoping.
Is anything retained afterwards?
No. Evidence is destroyed when the engagement closes.
Related guides
Scope a purple team exercise
Describe your detection setup and the threats you care about. We reply with written objectives, rules of engagement and a fixed fee before anything starts.
Request a written scope