Standards note
FFIEC penetration testing: what examiners expect to see
FFIEC penetration testing refers to testing that meets the expectations in the FFIEC IT Examination Handbook. So the work must fit the institution's risk, and the evidence must satisfy examiners.
- Written scope and rules of engagement
- PTES, OWASP and NIST SP 800-115
- Nothing retained after close
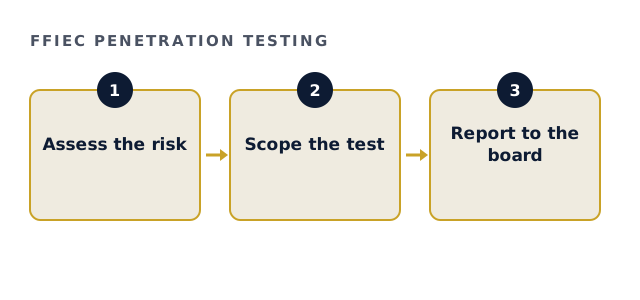
What the FFIEC handbook says about penetration testing
The Information Security booklet treats testing as part of an assurance programme. Therefore penetration tests sit alongside vulnerability assessments and audits, rather than standing alone.
The handbook expects testing to match risk. Also, it expects independence and clear reporting to management.
Scoping FFIEC penetration testing
Scope follows the institution's risk assessment. However, a few areas appear in most programmes.
| Area | Why examiners care |
|---|---|
| Internet banking and customer portals | Direct customer exposure |
| Internal networks | Insider and foothold risk |
| Third-party connections | Service providers widen the surface |
| Remote access | A frequent entry point |
FFIEC penetration testing readiness check
Tick what your programme already shows.
Your result appears here as you tick, so you can see what is still open.
Evidence for FFIEC penetration testing
Examiners look for a cycle, not a single report. So keep the scope, results, remediation and retest together.
- A risk-based testing plan
- Written scope and rules of engagement
- Findings rated by severity
- Remediation tracked to closure
- Reporting to senior management or the board
Independence and frequency
Testers should be independent of the systems they test. Because the handbook is risk-based, it does not fix one frequency for every institution. As a result, higher-risk systems are usually tested more often.
In addition, significant changes should trigger testing. The guidance itself is in the FFIEC Information Security booklet.
How Certus works
Every engagement runs under a signed scope and rules of engagement, following PTES, OWASP and NIST SP 800-115. Full engagements usually settle between $35,000 and $120,000, and the floor is $25,000. The bounded Security Posture Assessment starts at $4,500. Its fee is credited in full against a full engagement commissioned within ninety days.
FFIEC penetration testing questions
Does the FFIEC require FFIEC penetration testing every year?
The handbook is risk-based, so frequency follows risk rather than one fixed rule.
Who should perform FFIEC penetration testing?
A tester independent of the systems, internal or external.
What do examiners review after FFIEC penetration testing?
The plan, results, remediation and reporting to management.
Does a scan count?
No. Scans and penetration tests are separate parts of the programme.
Related guides
Scope FFIEC penetration testing to your risk
Describe the estate and the threat. We return a written scope that names each standard and what it governs, with a fixed fee. Nothing is tested before the owner signs.
Request a written scope